Download audit report
This document outlines the security review conducted by Nethermind Security for Worldcoin's WorldID Identity Manager smart contracts. The audit focuses on the updates made to the WorldID Identity Manager Implementation contract, with the goal of processing compressed proofs.
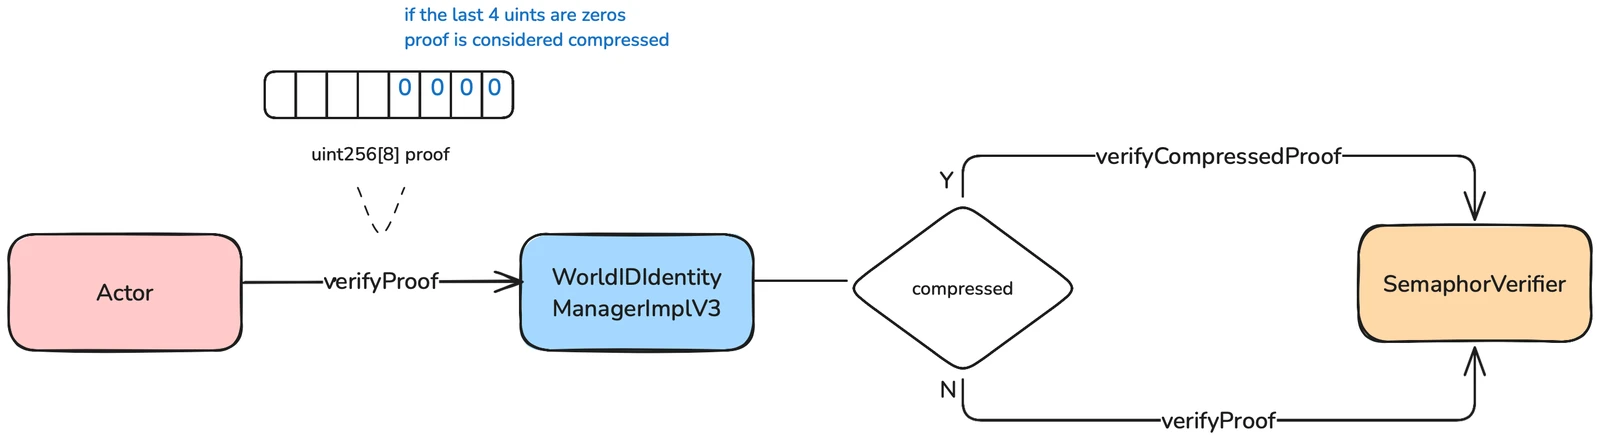
The existing World ID manager will be upgraded to the new WorldIDIdentityManagerImplV3 implementation. This update redefines the verifyProof function, enabling it to utilize the Semaphore Verifier's verifyCompressedProof function when a compressed proof is provided.
Moreover, the same updates have been implemented to the WorldIDBridge contract deployed on Worldchain, enabling it to use the compressed proof function.
The audited code comprises of 138 lines of code written in the Solidity language, and the audit was performed using (a) manual analysis of the codebase, (b) automated analysis tools, (c) simulation of the smart contract.
| Audit assessment | |
| Audit Type | Security Review |
| Draft Report | February 05, 2025 |
| Final Report | February 05, 2025 |
| Methods | Manual Review, Automated analysis |
| Repository | world-id-contracts, world-id-state-bridge |
| Initial Commit Hash | world-id-contracts: |
| Final Commit Hash | world-id-contracts: |
| Documentation Assessment | High |
| Test Suite Assessment | High |
Findings by severity
| # | Contract | LoC | Comments | Ratio | Blank | Total |
| 1 | src/WorldIDIdentityManagerImplV3.sol | 31 | 68 | 219.4% | 8 | 107 |
| 2 | src/interfaces/ISemaphoreVerifier.sol | 7 | 22 | 314.3% | 2 | 31 |
| Total | 38 | 90 | 236.8% | 10 | 138 |
| # | Contract | LoC | Comments | Ratio | Blank | Total |
| 1 | src/abstract/WorldIDBridge.sol | 88 | 116 | 131.8% | 44 | 248 |
| Total | 88 | 116 | 131.8% | 44 | 248 |
| # | Finding | Severity | Update |
| 1 | Comments/Natspec notes | Best Practices | Fixed |
The Worldcoin team introduced the WorldIDIdentityManagerImplV3 contract to upgrade the existing WorldIDIdentityManagerImplV2 implementation of the World ID identity manager. The primary goal of this upgrade is to enable the contract to process compressed ZK proofs. A proof is considered “compressed” when the last four uint values are zero, effectively reducing the proof size from 8 uints to 4 uints. Similar updates are implemented in the WorldIDBridge abstract contract.
The SemaphoreVerifier contract includes the verifyCompressedProof function that can be called directly to verify compressed proofs. As part of the upgrade, the verifyProof function has been modified to check whether the provided proof is compressed, and it will call the appropriate SemaphoreVerifier function based on the proof type.
function verifyProof(
uint256 root,
uint256 signalHash,
uint256 nullifierHash,
uint256 externalNullifierHash,
uint256[8] calldata proof
) public view virtual override onlyProxy onlyInitialized
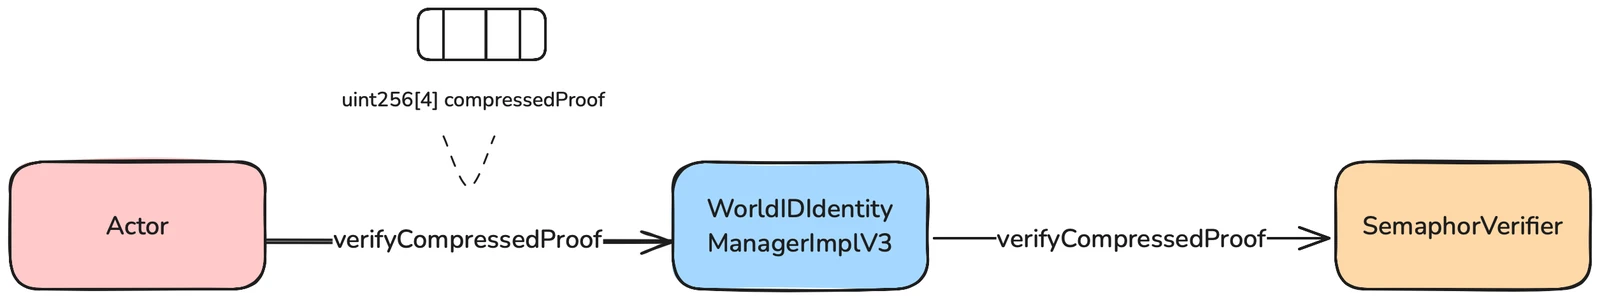
In addition, a new verifyCompressedProof function has been introduced, allowing to directly pass in a compressed proof for verification:
function verifyCompressedProof(
uint256 root,
uint256 signalHash,
uint256 nullifierHash,
uint256 externalNullifierHash,
uint256[4] calldata compressedProof
) public view virtual onlyProxy onlyInitialized 
It's important to note that this upgrade does not require reinitializing the contract. As such, the contract's initialized state ($._initialized) will remain set to 2. This poses no issues, as the change does not interfere with any other logic. Additionally, for a future V4 upgrade, simply adding reinitializer(4) will be sufficient.
The risk rating methodology used by Nethermind Security follows the principles established by the OWASP Foundation. The severity of each finding is determined by two factors: Likelihood and Impact.
Likelihood measures how likely the finding is to be uncovered and exploited by an attacker. This factor will be one of the following values:
When defining the likelihood of a finding, other factors are also considered. These can include but are not limited to motive, opportunity, exploit accessibility, ease of discovery, and ease of exploit.
Impact is a measure of the damage that may be caused if an attacker exploits the finding. This factor will be one of the following values:
When defining the impact of a finding, other factors are also considered. These can include but are not limited to data and state integrity, loss of availability, financial loss, and reputation damage. After defining the likelihood and impact of an issue, the severity is determined according to the table below.
| Impact / Likelihood | Low | Medium | High |
| High | Medium | High | Critical |
| Medium | Low | Medium | High |
| Low | Info / Best Practices | Low | Medium |
| Undetermined | Undetermined | Undetermined | Undetermined |
To address issues that do not fit a High, Medium or Low severity, Nethermind Security also uses three more finding severities: Informational, Best Practices, and Undetermined.
| File | Fix commit | Type | Status |
WorldIDIdentityManagerImplV3.sol | effe83464bdbb4 | Best Practices | Fixed |
The following are observations about the comments and Natspec on the WorldIDIdentityManagerImplV3 file:
WorldIDIdentityManagerImplV3
- Comment on L21 stats that the contract inherits from `WorldIDIdentityManagerImplV1`.
However, it actually inherits from `WorldIDIdentityManagerImplV2`.
WorldIDIdentityManagerImplV3.verifyProof
- Comment on L61: "The of the Merkle tree" should be corrected to "The root of the Merkle tree".
WorldIDIdentityManagerImplV3.verifyCompressedProof
- Comment on L89: "The of the Merkle tree" should be corrected to "The root of the Merkle tree".Recommendation
Consider addressing the comment and Natspec observations made above.
Software documentation refers to the written or visual information that describes the functionality, architecture, design, and implementation of software. It provides a comprehensive overview of the software system and helps users, developers, and stakeholders understand how the software works, how to use it, and how to maintain it. Software documentation can take different forms, such as user manuals, system manuals, technical specifications, requirements documents, design documents, and code comments. Software documentation is critical in software development, enabling effective communication between developers, testers, users, and other stakeholders. It helps to ensure that everyone involved in the development process has a shared understanding of the software system and its functionality. Moreover, software documentation can improve software maintenance by providing a clear and complete understanding of the software system, making it easier for developers to maintain, modify, and update the software over time. Smart contracts can use various types of software documentation. Some of the most common types include:
These types of documentation are essential for smart contract development and maintenance. They help ensure that the contract is properly designed, implemented, and tested, and they provide a reference for developers who need to modify or maintain the contract in the future.
The documentation for the World identity manager implementation upgrade is contained in the provided PR description in addition to the README file in the project's GitHub repository.
The PR description is thorough and informative. It includes a clear breakdown of the changes made, the impact on the existing codebase, and specific actions required for deployment.
The README file delivers an in-depth explanation of the WorldID Semaphore Contracts, clearly outlining the key components and how they interact. It also includes a section dedicated to explaining the development dependencies, as well as step-by-step instructions on how to build and test the code.
The added functions are thoroughly documented. Each function includes detailed comments that explain the logic behind its implementation and the significance of each parameter.
The test suite for the World Identity Manager contracts is comprehensive, covering both public and internal functions. For the audited changes, new tests have been added to upgrade the implementation to version 3 (v3), as well as to cover the flow of validating compressed proofs.
| 96Tests passed | 0Failed |
The complete test output is in the full report.
As auditors, we recommend that any changes or updates made to the audited codebase undergo a re-audit or security review to address potential vulnerabilities or risks introduced by the modifications. By conducting a re-audit or security review of the modified codebase, you can significantly enhance the overall security of your system and reduce the likelihood of exploitation. However, we do not possess the authority or right to impose obligations or restrictions on our clients regarding codebase updates, modifications, or subsequent audits. Accordingly, the decision to seek a re-audit or security review lies solely with you.
This report is based on the scope of materials and documentation provided by you to Nethermind in order that Nethermind could conduct the security review outlined in 1. Executive Summary and 2. Audited Files. The results set out in this report may not be complete nor inclusive of all vulnerabilities. Nethermind has provided the review and this report on an as-is, where-is, and as-available basis. You agree that your access and/or use, including but not limited to any associated services, products, protocols, platforms, content, and materials, will be at your sole risk. Blockchain technology remains under development and is subject to unknown risks and flaws. The review does not extend to the compiler layer, or any other areas beyond the programming language, or other programming aspects that could present security risks. This report does not indicate the endorsement of any particular project or team, nor guarantee its security. No third party should rely on this report in any way, including for the purpose of making any decisions to buy or sell a product, service or any other asset. To the fullest extent permitted by law, Nethermind disclaims any liability in connection with this report, its content, and any related services and products and your use thereof, including, without limitation, the implied warranties of merchantability, fitness for a particular purpose, and non-infringement. Nethermind does not warrant, endorse, guarantee, or assume responsibility for any product or service advertised or offered by a third party through the product, any open source or third-party software, code, libraries, materials, or information linked to, called by, referenced by or accessible through the report, its content, and the related services and products, any hyperlinked websites, any websites or mobile applications appearing on any advertising, and Nethermind will not be a party to or in any way be responsible for monitoring any transaction between you and any third-party providers of products or services. As with the purchase or use of a product or service through any medium or in any environment, you should use your best judgment and exercise caution where appropriate. FOR AVOIDANCE OF DOUBT, THE REPORT, ITS CONTENT, ACCESS, AND/OR USAGE THEREOF, INCLUDING ANY ASSOCIATED SERVICES OR MATERIALS, SHALL NOT BE CONSIDERED OR RELIED UPON AS ANY FORM OF FINANCIAL, INVESTMENT, TAX, LEGAL, REGULATORY, OR OTHER ADVICE.
The Leading Engineers of Blockchain Infrastructure